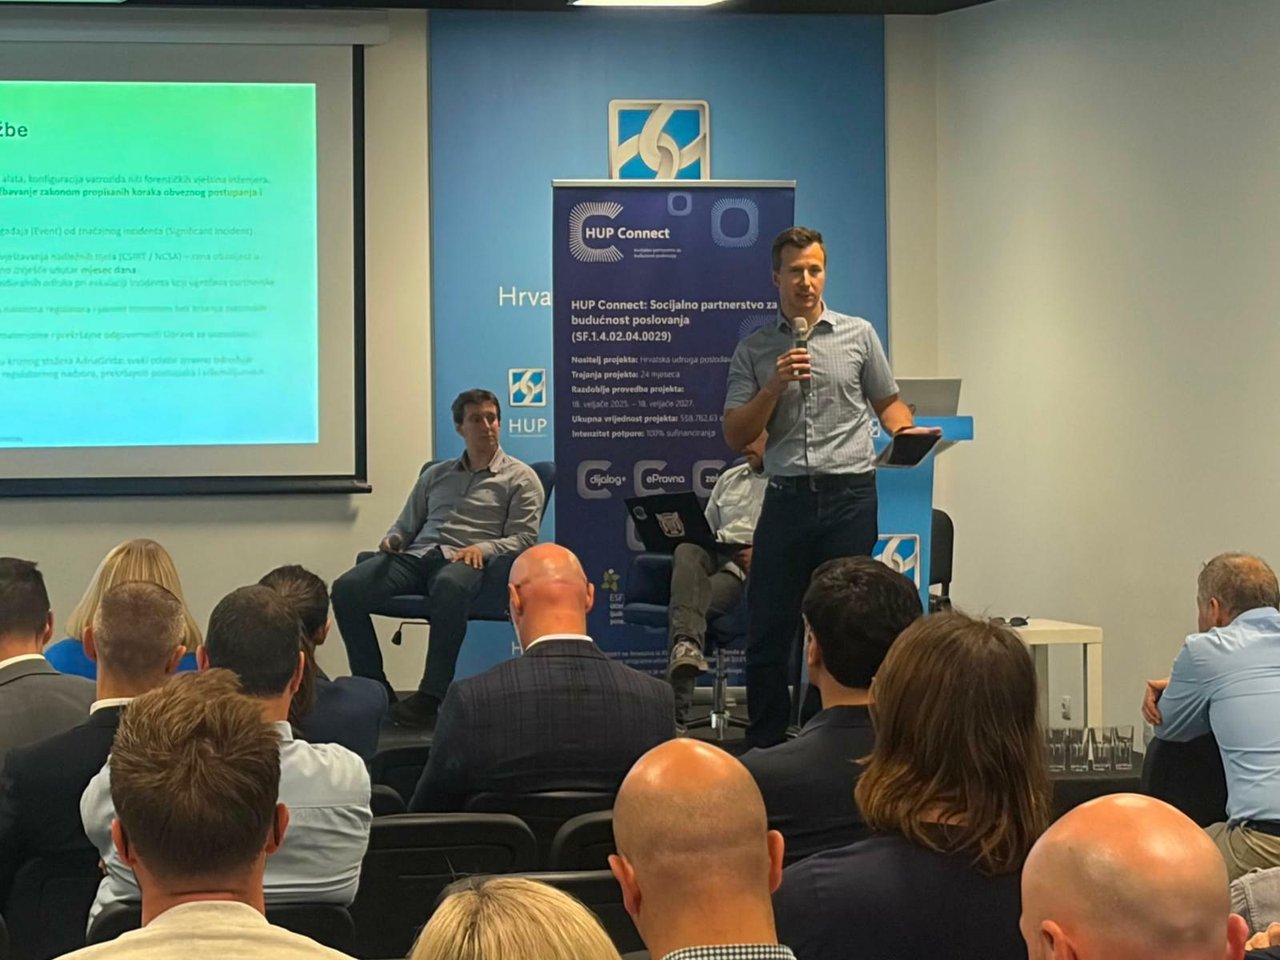
A cyber incident can halt business operations in a very short time, jeopardizing data, relationships with customers and partners, finances, and the reputation of the company. That is why cybersecurity is no longer the responsibility of just the IT department, but one of the important issues of business management,” emphasized Jasminka Martinović, director of the HUP-ICT Association, Jasminka Martinović at the HUP Cyber Practicum – “Through experience, practice, and education to cyber-resilient business,” organized by the HUP-ICT Association in Zagreb.
The Cyber Practicum brought together experts from the private and public sectors with the aim of bringing cybersecurity closer to business reality: less through theory and more through concrete experiences, incident simulation, and practical answers to questions that companies face before, during, and after a cyber attack.
– Cybersecurity is no longer exclusively a matter for IT professionals, but one of the key prerequisites for business continuity, data protection, user trust, and the reputation of every organization. In the context of the accelerated development of new technologies, increasingly complex threats, and growing regulatory requirements, the best defense is not only technology but also knowledge, preparedness, and cooperation between the public and private sectors.
Through the exchange of experiences, education, and building strong partnerships, we can increase the resilience of the Croatian economy to cyber risks, which we have been continuously doing for the past three years through the work of the HUP Coordination for Cybersecurity,” said Martina Dragičević, on behalf of the HUP Coordination for Cybersecurity.
The focus was on how to prepare for an incident, who must make decisions when it occurs, how to protect business and reputation, and how to communicate with employees, users, partners, and relevant institutions.
A cyber incident requires quick decisions
The central part of the Cyber Practicum was the Table Top exercise “How to manage a cyber incident?” led by Andro Galinović and Jurica Čular from Infobip and Riko Luša from Končar, with the participation of representatives from the National Cyber Security Center (NCSC-HR).
Participants went through the legal obligations of incident reporting, best practices, assessing the scale of the incident, how to communicate with key stakeholders, and the consequences of incorrect actions through an interactive simulation. The goal of the exercise was not to provide pre-known answers but to show what decision-making and incident management look like under conditions of incomplete information and time pressure. This also emphasized one of the key messages of the Practicum: an organization cannot reliably assess its readiness solely based on procedures, but it also needs to be verified through exercises.
– One of the most frightening aspects of a cyber incident for many companies is navigating through regulatory complexity and the implications of reporting the incident to the regulator. There are many prejudices about this process and a lack of understanding of why, in addition to legal obligations and responsibilities, reporting and sharing information are beneficial for society as a whole.
Through this exercise, we wanted to provide participants with a new perspective and better understanding of the process and, with direct support from the National Cyber Security Center, clarify often unclear edge cases. The goal was to ensure that companies clearly understand when, to whom, and how to report an incident in the event of a cyber incident,” said Andro Galinović, director of corporate security at Infobip.
Special attention was paid to the challenges faced by small and medium-sized enterprises, which must respond to increasing security demands with limited financial and human resources. Luka Matić from NEP-054 spoke about prioritizing and practical steps that the SME sector can take to gradually increase its level of cyber resilience. Representatives from the Information Systems Security Agency (ZSIS) and Marko Žalac from Deloitte discussed what the new regulatory framework means in practice.
Timely preparation is key
The focus was on questions about how inspections and audits look according to the Cybersecurity Regulation, what is checked, and how organizations can prepare in a timely manner. Tomislav Bronzin from Citus spoke about what owners, directors, and management need to decide before an incident occurs and how pre-established responsibility and preparation can reduce the impact of attacks on business and reputation.
The Cyber Practicum concluded with a discussion with Vlatka Marčan from the National Coordination Center for Cyber Security (NKS) about the support available to Croatian organizations, including education, competency development, and funding opportunities for activities and projects in the field of cybersecurity.
The key message of the Cyber Practicum is that cyber resilience is built before an incident – through the preparation of people, clear responsibilities, established processes, and their regular testing.