
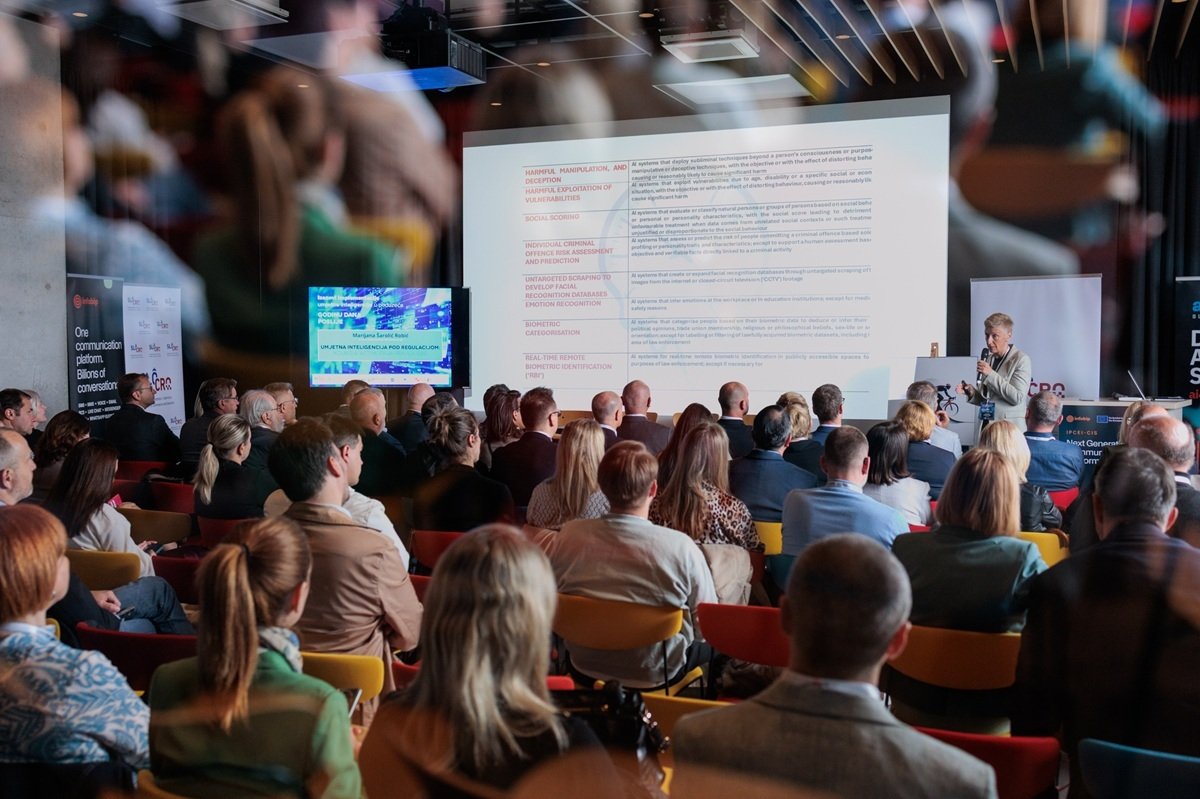
The European Artificial Intelligence Act, whose origins date back to 2018, came into force in all member states of the European Union in August of last year. While it brings a range of opportunities for the development of this rapidly growing technology, there are also new rules of the game that all companies must adhere to. As is well known, the European law on artificial intelligence defines five levels of risk for AI systems, from those that are completely prohibited, through high-risk, to those that are for general use and acceptable. However, as pointed out by Marijana Šarolić Robić, a lawyer and vice president of the Cro Startup Association, at today’s conference on the challenges of implementing AI in businesses organized by Infobip, the SLO CRO Chamber of Commerce, and the Embassy of the Republic of Slovenia in Zagreb, companies must thoroughly study the AI Act as the penalties for non-compliance are extremely strict.
Namely, penalties can reach up to 35 million euros or seven percent of a company’s annual revenue, which is more than in the case of the previous European data protection law, GDPR. However, penalties are not the reason for the introduction of artificial intelligence regulation, emphasized Šarolić Robić. Their purpose is to ‘force’ businesses to comply with European legislation, but not to fear penalties.
– The regulator has introduced the same system that has already been tested on GDPR, only the penalties are higher than those stated for GDPR. They have also made a distinction between small and medium-sized enterprises and large ones, so the penalties for SMEs have been modified. However, they are still equally dangerous – says Šarolić Robić.
Decision-making is accelerating
During the subsequent panel discussion, Davor Aničić, director of VelebitAI and a member of the board of the Croatian Artificial Intelligence Association CroAI, explained the risks that these penalties pose for small and medium-sized enterprises.
– Fortunately, the AI Act recognizes small companies in relation to GDPR and prescribes somewhat lower penalties. For small companies, it speaks of a percentage of global turnover, not an absolute amount, as in GDPR where the absolute amount could exceed the total revenue of the company ever. However, this percentage is still significant and carries six to seven percent of revenue. The question is what the profit margin of the company is – explained Aničić, who represents CroAI in the working group of the Ministry of Justice, Administration, and Digital Transformation that is working on drafting the Croatian law on the application of the AI Act.
—

—
Their proposal is that, contrary to GDPR, for small companies, no decision of the act should be immediately enforceable, but that they have the right to appeal the decision, which would delay the enforceability of that decision, i.e., the payment of the penalty.
The AI Act is also a challenge for the state, admitted Damir Habijan, the Minister of Justice, Administration, and Digital Transformation, at the conference, considering that the transposition of the act into Croatian legislation must ensure the protection of citizens’ privacy and security, while on the other hand, it must not happen that companies leave Europe because of it.
Precisely because of the excessive regulation of the AI Act, which Habijan assessed as the biggest challenge, but also due to the rapid development of artificial intelligence, the Government launched the drafting of the National Plan for the Development of Artificial Intelligence by 2032 last week. Initially, a strategy for the development of AI was planned, but they realized that such a document is too closed and cannot keep up with the rapid changes in this technology. Therefore, the law-making process will also be faster, Habijan announced.


