
The largest known hacking attacks include those on Yahoo in 2013, when all three billion user accounts were affected, and in 2014, when 500 million users were compromised. Stronger cyber attacks included the ransomware WannaCry, which hit more than 200,000 computers in 150 countries in 2017, and the 2021 attack on the American Colonial Pipeline system, which caused fuel shortages.
To enhance cybersecurity and counter hackers, the European Union adopted the NIS2 directive – the Directive on the Security of Network and Information Systems, which builds on previous legislation in this area. The NIS2 directive came into effect in January 2023, and in accordance with it, a new Cybersecurity Act was published in Croatia in 2024, under which organizations must consider the vulnerabilities of direct suppliers and service providers, their overall product quality, and security practices.
Modern Data Centers
There are several requirements for organizations set by the NIS2 directive. To thwart cyber intrusions, organizations must conduct risk assessments and develop appropriate security policies and measures, and the awareness of company management regarding risks and protective measures must be very high. It is also necessary for key and important entities to publish information about security incidents that significantly affect service supply or service recipients, according to prescribed guidelines and reporting deadlines. In the event of a breach in the system, teams for crisis response must be designated, and security procedures and system recovery must be considered.
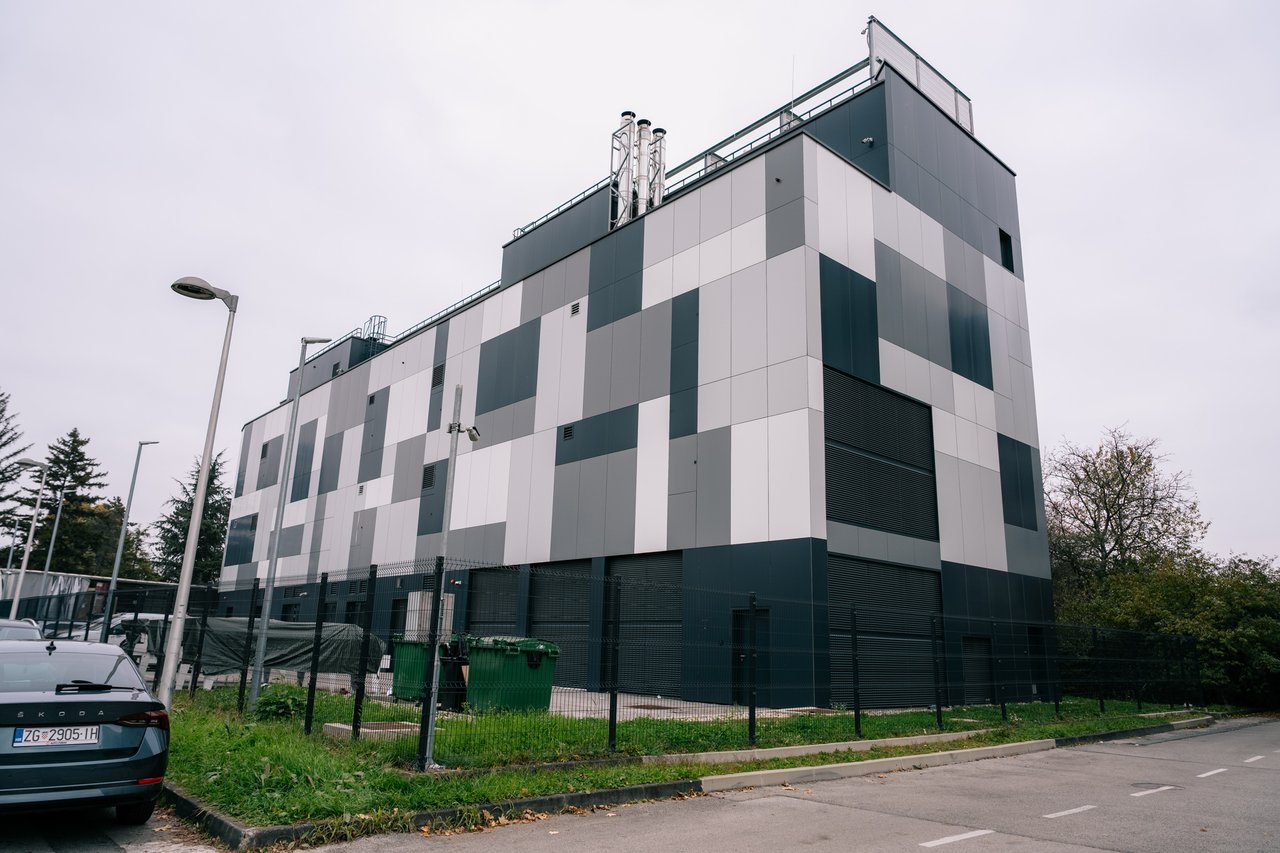
To better prepare entrepreneurs for the provisions of the NIS2 directive, A1 Croatia offers users a range of additional solutions such as a Security Operations Center (SOC), automated penetration testing, a company vulnerability scanning system, and defense against distributed denial-of-service attacks or resource protection, management, and access control. Furthermore, as Croatia increasingly becomes a candidate for a regional data hub due to its strategic geographical position, developed and redundant infrastructure, and growing investments in digital transformation, modern data centers like the A1 Data Center are opening. It was opened in 2021 and already received a Tier 3 design certification at that time, and a year later, it received the PCI DSS certification, confirming the highest level of security. Following this, the Tier 3 Facility certification was awarded, placing the A1 Data Center among only two such centers in Croatia and making it the only one in the Zagreb area with that level of protection.


