
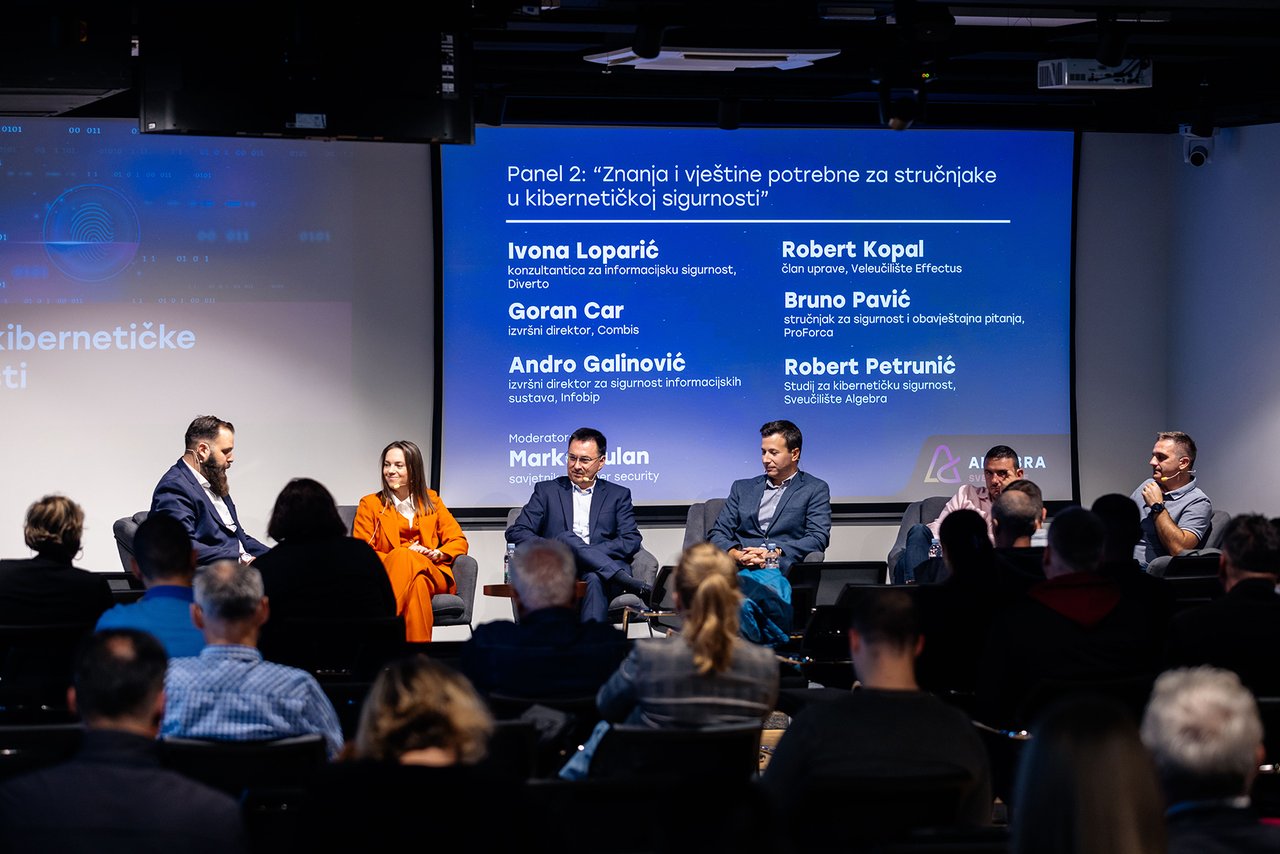
On Friday, the first conference on the new Cybersecurity Regulation, which was put out for public consultation last Tuesday, was held in a packed Algebra Spark Space. Among other topics, the discussion focused on the global need for raising competencies, retraining, and additional education for experts in the field of cybersecurity. The conference brought together experts and industry representatives who exchanged experiences, knowledge, and perspectives on the new legal frameworks regulating cybersecurity.
On Tuesday, October 8, 2024, the Cybersecurity Regulation, enacted under the Cybersecurity Act, was published for public consultation. It prescribes criteria for the categorization of entities and the measures or controls that obligated parties must implement, as well as the criteria for reporting significant incidents. In this process, after entities are informed by the competent authority of their category and the measures applicable to them, it is crucial to understand the scope of implementing specific measures, following a prior assessment (gap analysis) of the current maturity level of the applied measures and those that each entrepreneur needs to implement, along with planning an adequate budget for the implementation of specific measures.
– Given the constant advancement of technology, cyber threats are becoming increasingly sophisticated and harder to detect. Today’s attacks can involve highly sophisticated methods such as ‘zero-day’ exploits, which exploit vulnerabilities in software that are not yet known or patched by the manufacturer. Additionally, advanced phishing is used to target specific individuals through tailored messages that appear extremely convincing. Social engineering techniques have also advanced; attackers conduct thorough preparations to make their methods as effective as possible. The greatest threats still come from individuals who are not sufficiently educated and thus make mistakes – emphasized Robert Petrunić, a lecturer at the newly launched Cybersecurity Study at Algebra University.
Irena Weber, the CEO of HUP, had the honor of opening the conference, and in her introductory speech, she highlighted the perspective of entrepreneurs in digital transformation and the development of cybersecurity.
– Cybersecurity is no longer considered solely within the IT sector, but much broader. HUP participated in drafting the law to assist companies and the entire economy. The provisions help entrepreneurs adapt their business and ensure a secure digital future for all. The new Cybersecurity Act brings numerous obligations but also opportunities. By introducing a higher level of security, our companies have the chance to secure customer trust and become more competitive in the global market. The law provides us all with opportunities for further growth, and this conference and additional education on cybersecurity are a significant and important step in the right direction, and I believe it will ensure a secure future for all of us – said Weber.
With the Cybersecurity Act, on February 15, the functionality of a central state body for cybersecurity was established, which will be performed by SOA, and for this purpose, the existing Cybersecurity Center of SOA will be transformed into the National Cybersecurity Center (NCSC-HR). On this occasion, Aleksandar Klaić from the Cybersecurity Center of SOA reflected on the detection, early warning, and protection against cyber attacks and presented a development plan and awareness-raising for the broader population about cybersecurity.
– Due to the seriousness of the entire process, everything needs to be accompanied in a new organizational way in which the enacted law will assist us. SOA will focus in the coming weeks and months on the core issues occurring in cybersecurity worldwide, namely, insufficient awareness of cybersecurity risks. However, this is not only true for Croatia or the EU but for most countries in the world – Klaić began.
– We must consider the entire regulatory framework. A significant amount of work awaits us, but the deadlines are set liberally, not to avoid work, but to develop a culture of risk management and to raise the maturity level of cybersecurity in all key segments, whether they are state or private entities – he explained, adding that the Ministry of Defense (MORH) and the Ministry of the Interior (MUP) provide support. Indeed, MORH plays an important role in the military or defense sector, while MUP combats cybercrime.
– The process must be completed by April 2025, as we must have an initial list for the European Commission by then. The initial categorization will be conducted no later than March 2025, by which time you will receive a notification about the categorization, and then the obligations for entrepreneurs will commence. After April 2025, the implementation of measures in entities will follow within a year. You had a year to study the Law, and now you have another year to implement the measures. The deadlines are not very tight but are liberal because we expect a partnership relationship from the entire society. Measures and penalties must be prescribed because the law is nothing but a security policy – Klaić conveyed to the gathered entrepreneurs, adding that if the mentioned measures are not implemented, economic growth will be impossible.
Krešimir Šipek from the Institute for Information Security spoke about the implementation of self-assessment of cybersecurity. Self-assessment of cybersecurity in key entities can be conducted as preparation for the implementation of a cybersecurity audit. It should be conducted at least once every two years with the help of internal resources or external service providers. Self-assessment is crucial for establishing systematic risk management at the organizational level, better understanding and protection of one’s IT infrastructure, and raising awareness of cybersecurity among employees, as well as strengthening the resilience of the entire digital society, which is one of the key points of the NIS2 directive.


