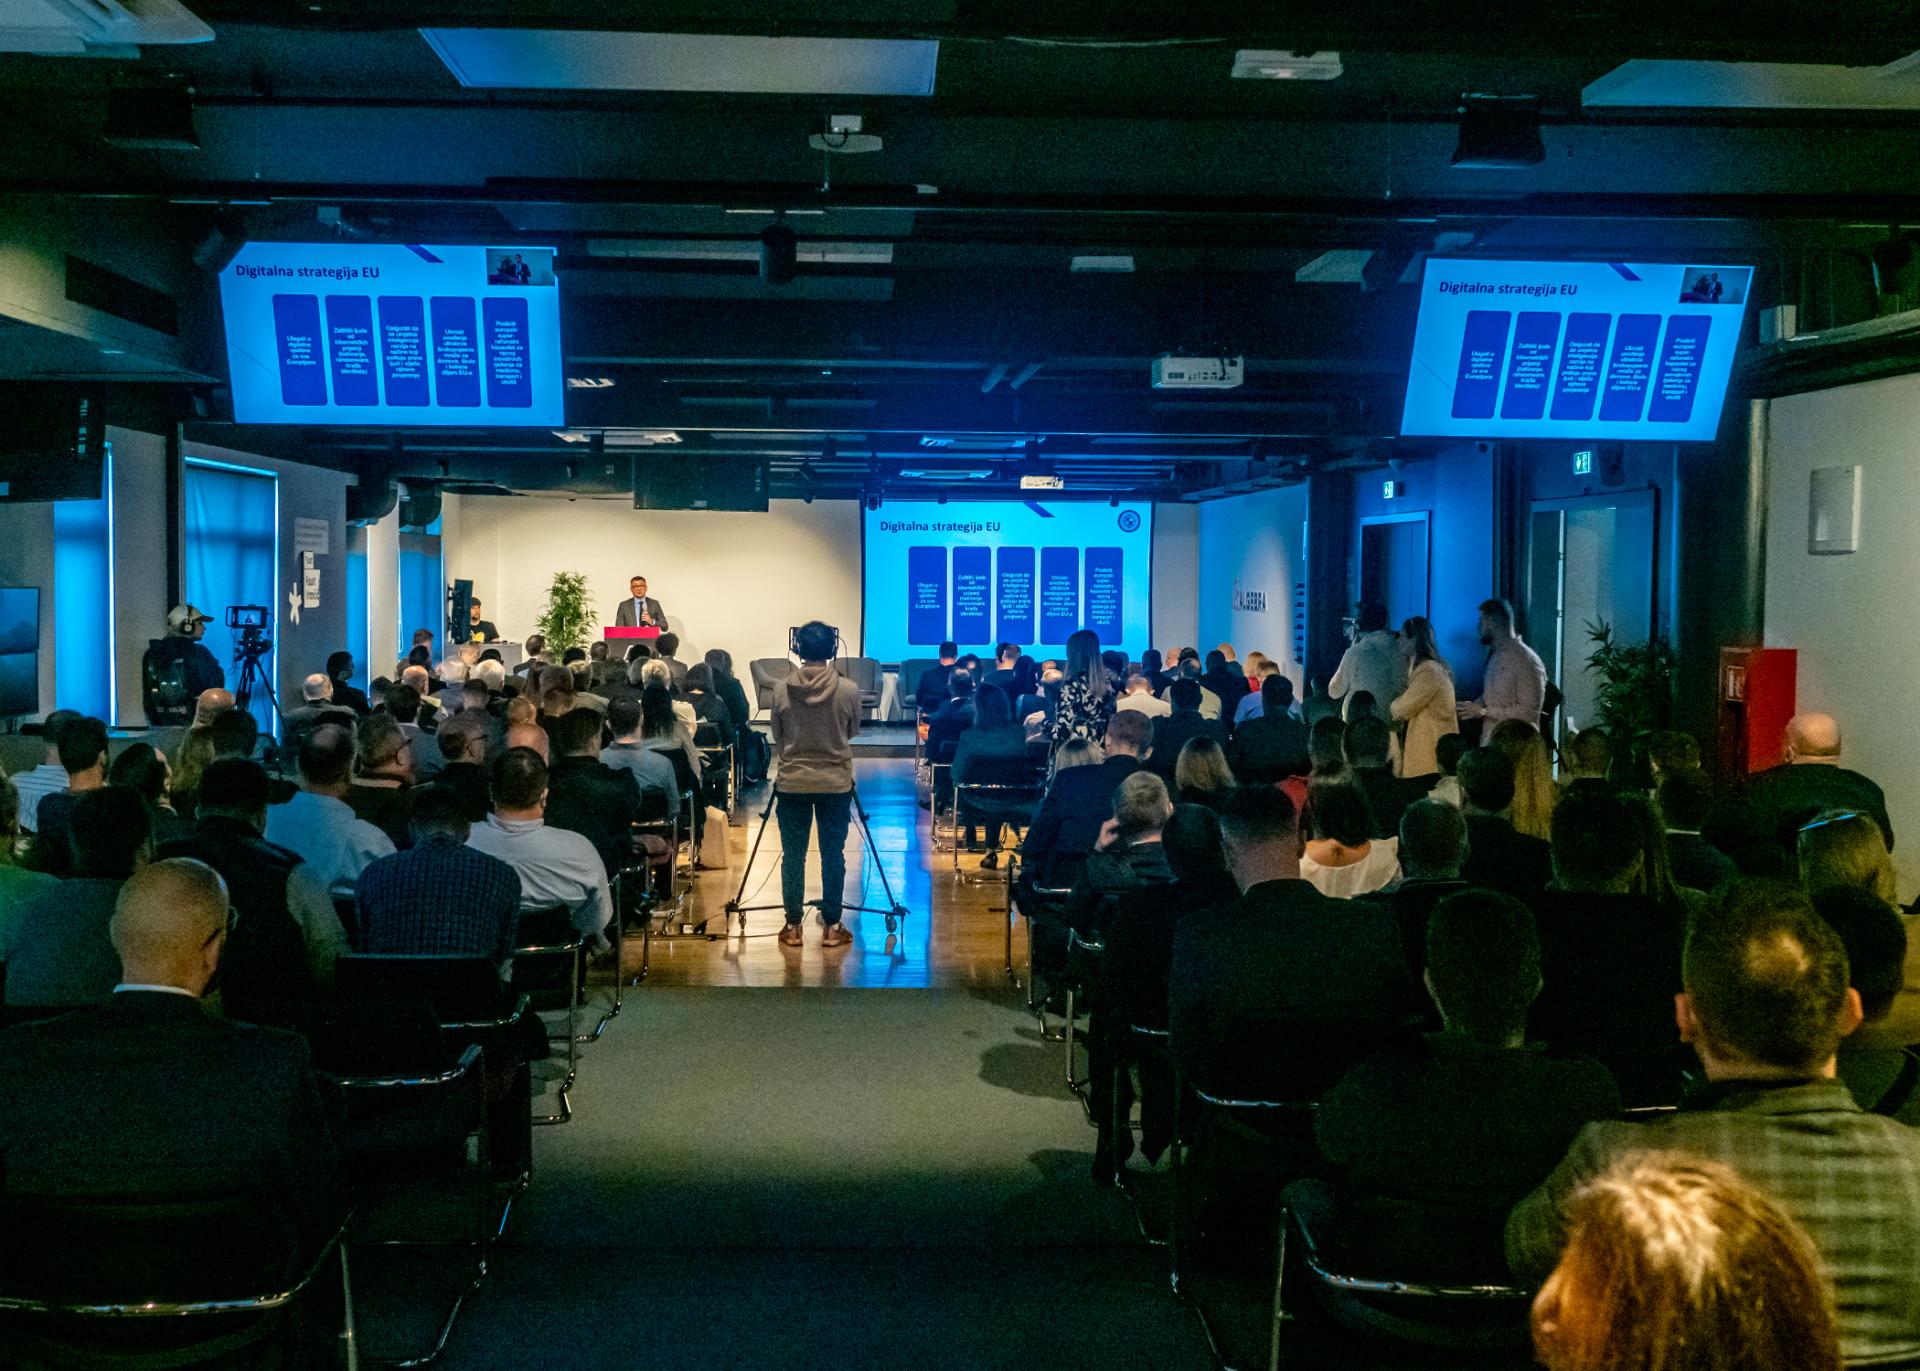
The new Cybersecurity Act, aligned with the European Commission’s NIS2 Directive, will affect three to four times more companies in Croatia than has been the case so far, which means that entrepreneurs will need to invest more resources in ICT security. As business digitalization increases, so do the threats from cyberattacks, but in addition to adapting to the new law, it also means new opportunities for Croatian companies. As highlighted today during a panel discussion at the conference on the new law held at Algebra University, the increased demand for cybersecurity solutions will also boost demand for companies specializing in this area, presenting an opportunity for the development of the Croatian economy.
Investment will be necessary, but it is difficult to estimate how much, as it depends on how much individual companies have already invested in cybersecurity, said Boris Bajtl, Vice President of the Croatian Institute for Cybersecurity, Head of the Cybersecurity Department at Atos Croatia, and a member of the Executive Board of HUP-ICT. There is room for improvement in cybersecurity within companies even without investments, Bajtl noted, and economic opportunities include the creation of new jobs and drawing funds from EU sources.
– The new law will increase demand for these services, which will automatically increase supply, and that is an opportunity – said Bajtl, adding that the Croatian Employers’ Association will be involved in consulting during the drafting of regulations, thus having the opportunity to convey employers’ requirements and participate in that process.
Market Gap
Compliance audits with NIS2 laws will be conducted by legal entities approved for this purpose, explained Dr. Aleksandar Klaić from the Cybersecurity Center of the Security and Intelligence Agency (SOA), referring to hundreds of entities and a large number of such activities for all companies that decide to go in that direction. All companies in the ICT sector will have to comply with the NIS 2 law, regardless of size, and they also have an additional opportunity to certify their cybersecurity services in a certain way and apply them as such through the EU register not only in Croatia but also beyond.
– This is a significant change because today you cannot offer these services in a standardized way as they do not exist – Klaić explained, adding that compliance with the NIS2 directive will also bring better competitiveness in tenders for EU funding.
– At the EU level, there are not many companies that can provide advanced services, and this area is relatively free both at the level of large and small states – Klaić said.
—
—
Companies will gradually implement the directive, Klaić noted, and the entire process should take place over a year from the adoption of the law.
– Only upon receiving notifications should individual entities from any sector take action and align their cybersecurity systems, for which they have one year. Thus, in that notification, entities will also receive technical information – Klaić added.
Companies and state bodies that already apply the ISO/IEC 27001 international standard for information security management will be at an advantage as they will have little to adjust according to NIS 2.